
Document management SaaS / Engineering case study
Smart Document Vault
Multi-tenant document-management API with secure isolation.
Project facts
Tenant-aware design
Document-processing safety
API contract alignment
Isolation-focused validation
Overview
A public architecture overview of a tenant-aware document service. Tenant resolution, policy logic, storage topology, and processing rules are intentionally omitted.
01 / Context
The problem
A shared document platform must preserve customer isolation and handle document processing safely without making private policy or infrastructure assumptions part of the public interface.
My role
I contributed tenant-aware access controls, secure document processing, contract-aligned API behavior, and isolation-focused tests. The case study excludes customer identifiers, policy rules, storage paths, and security configuration.
Constraints
Customer contexts required reliable separation, document processing needed privacy-conscious handling, and public documentation could not expose security configuration or storage design.
02 / Engineering
Technical decisions
The design applies defense-in-depth to document access and processing, with isolation enforced by the backend and longer-running work handled asynchronously where appropriate.
Exact tenant resolution, policy evaluation, storage topology, security configuration, failure policy, and recovery procedures remain private.
Validation
Validation focused on representative same-context and cross-context requests, public availability behavior, and documented API responses.
03 / Delivery
What the project delivers
The project provides a security-first foundation for tenant-isolated document management with automated access-boundary and API-contract coverage. It does not claim a public launch, customer volume, or security certification.
Lessons and next steps
Isolation and processing safety work best when treated as system-wide design concerns rather than isolated endpoint checks.
Architecture overview
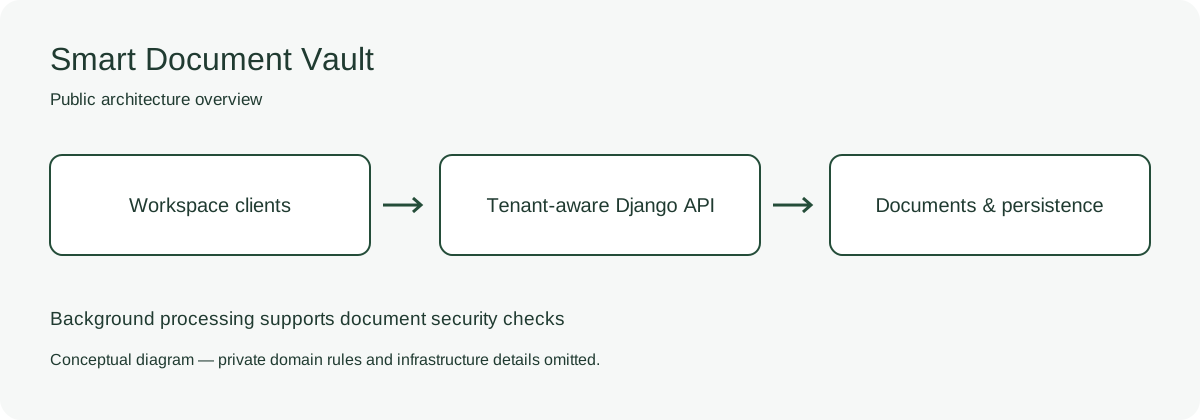
The Django backend applies defense-in-depth to customer isolation, document access, and supporting processing. Policy evaluation, storage design, and failure handling remain private.
This public summary omits private domain rules, data relationships, security policies, and operational details.
Engineering challenges
Maintaining customer isolation
Context: Shared infrastructure must preserve separation between customer contexts.
Decision: Apply defense-in-depth in the backend without exposing policy mechanics publicly.
Trade-off: Defense-in-depth adds implementation and validation work but reduces reliance on any single control.
Validation: Validation focused on representative same-context and cross-context requests.
Handling document processing safely
Context: Document processing must preserve privacy and predictable API behavior.
Decision: Separate processing concerns from public access while keeping private failure policies undisclosed.
Trade-off: Separating processing improves safety boundaries while adding operational coordination.
Validation: Validation focused on public availability behavior across processing outcomes.
Technical focus
Django REST Framework
Tenant-aware authorization
Asynchronous security processing
Documented API contracts
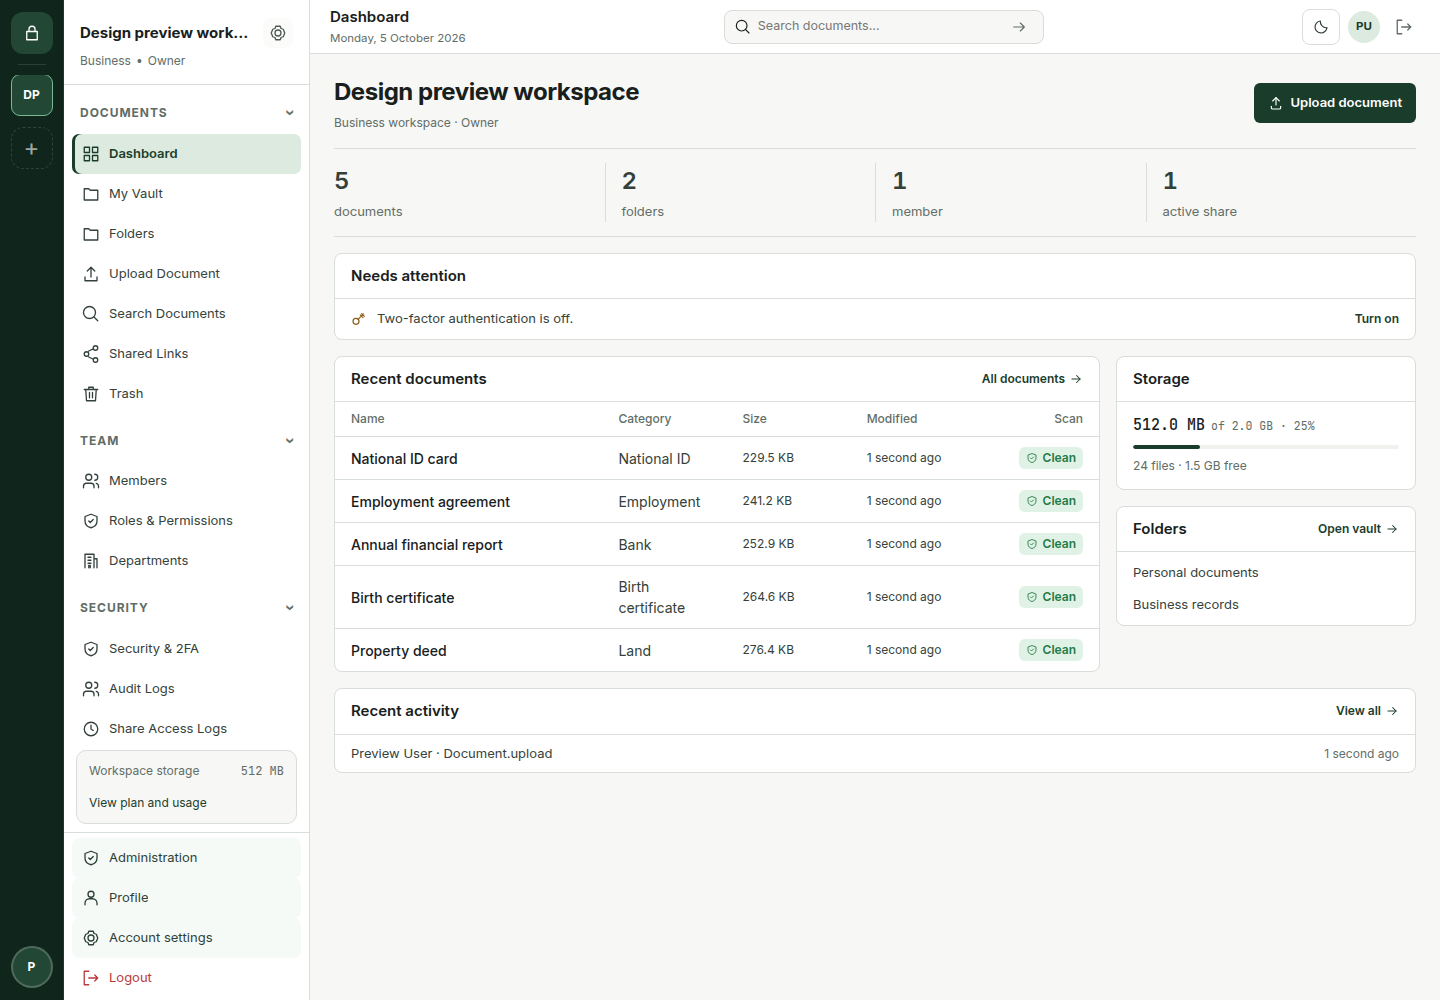
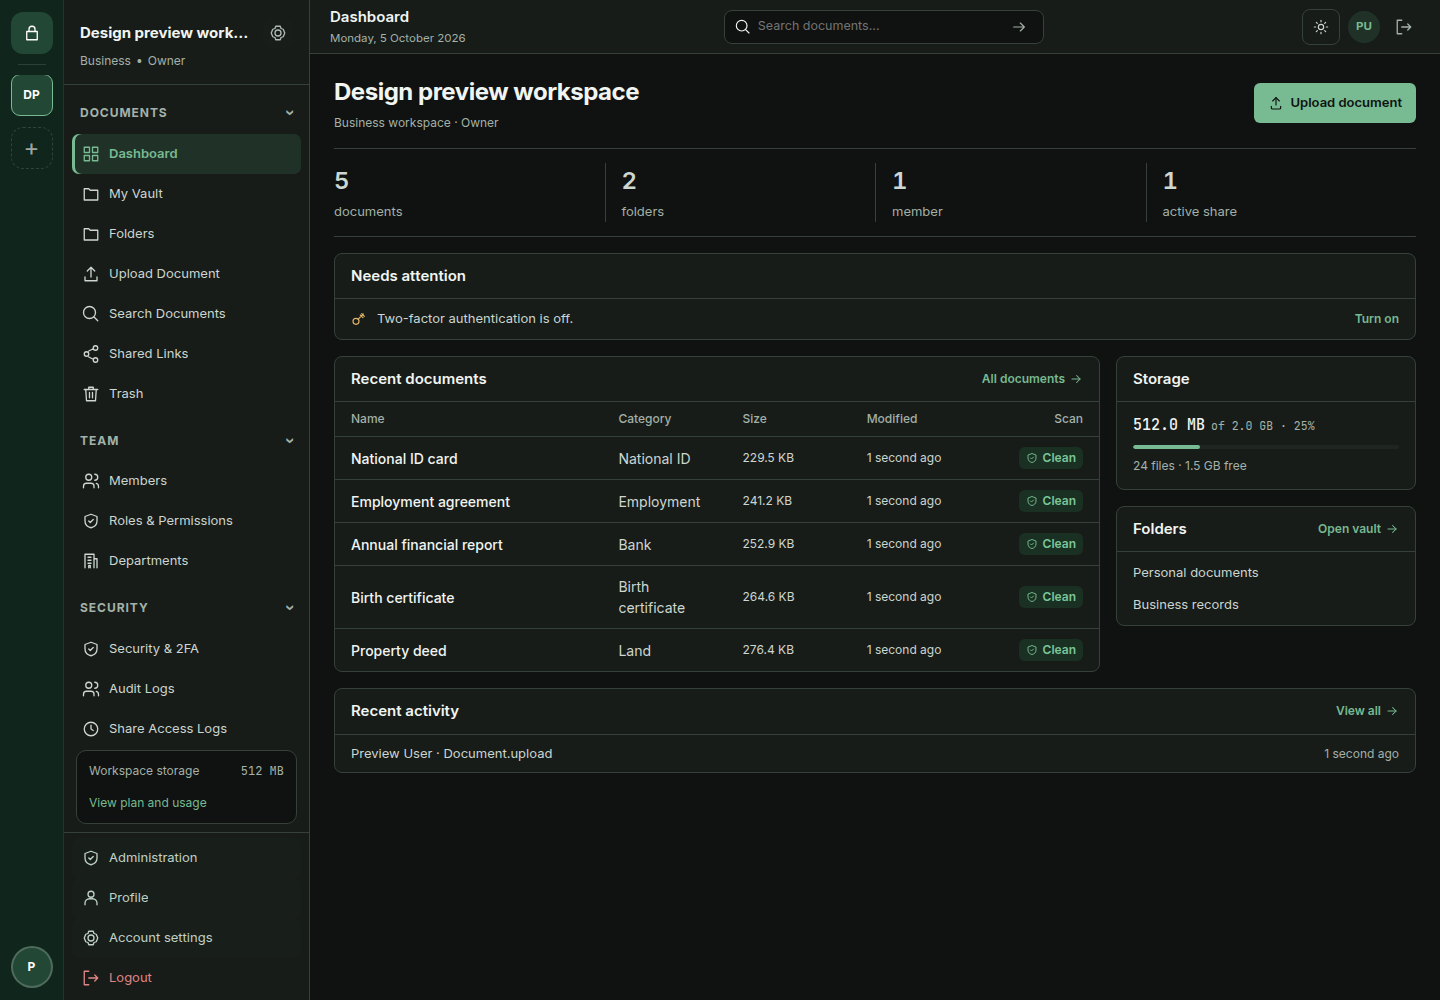
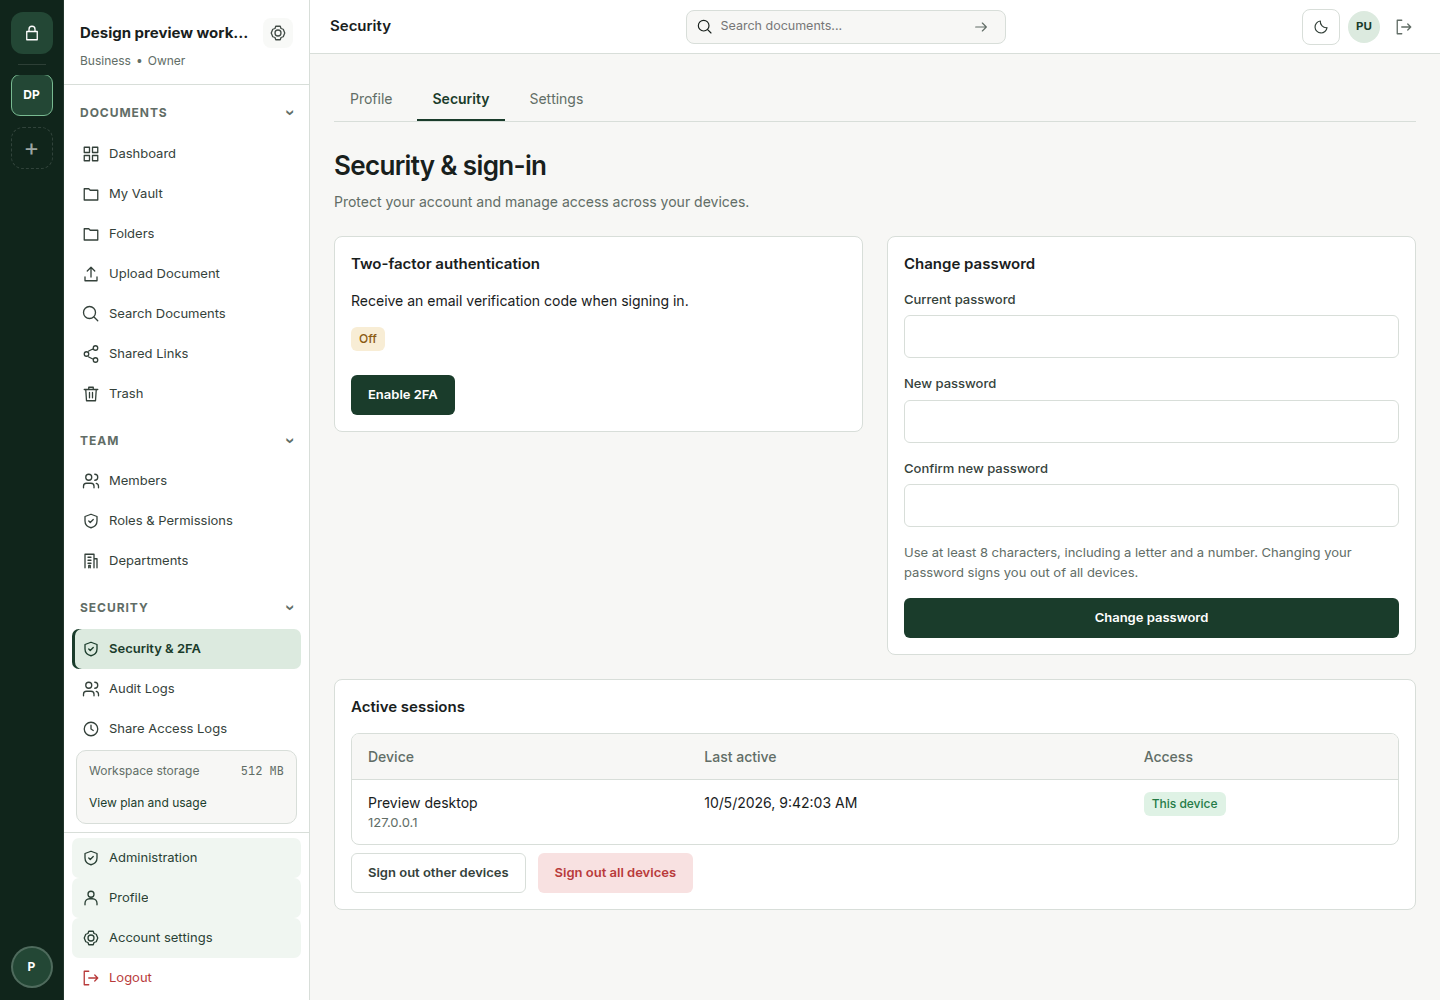
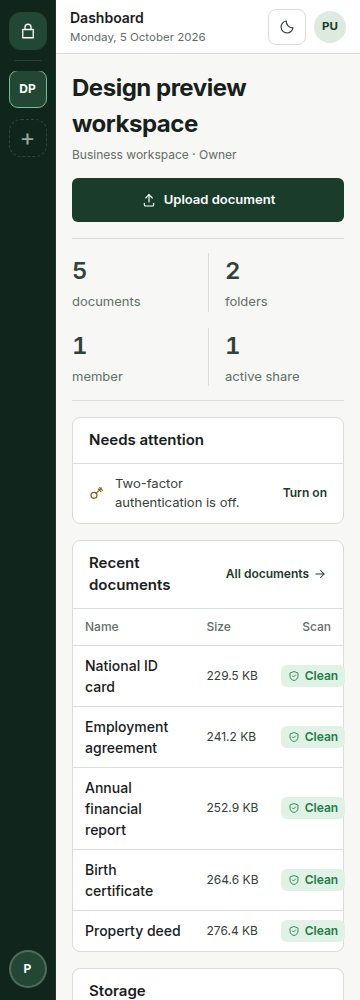
Project screenshots
Application screenshots using synthetic demo data.
Public architecture diagram
Demo walkthrough
A screenshot montage using synthetic demo data.
Interested in work like this?
This public case study demonstrates engineering judgment without exposing internal business logic.
Let’s start a conversation ↗